Security
Your clients' figures, held with care
A practice trusts us with every client it has. Each measure on this page runs in the product today, explained in plain words, and the page says what we do not have yet.
01
Where your clients' data lives
In the EU, and kept apart from every other practice by the database itself.
Hosted in Frankfurt
The app runs in Frankfurt and so does its database. Documents are stored in the EU, in buckets that may hold data in the EU only.
One practice, one boundary
Row level security in the database keeps each practice's rows apart, so a fault in a screen cannot show one practice another's clients.
Encrypted at rest and in transit
Every connection uses TLS, and storage is encrypted. HMRC tokens and second factor secrets are encrypted again, each under its own key and purpose.
02
Signing in
Every member of staff proves who they are twice, and the actions that cannot be undone ask again.
Two factors for every member of staff
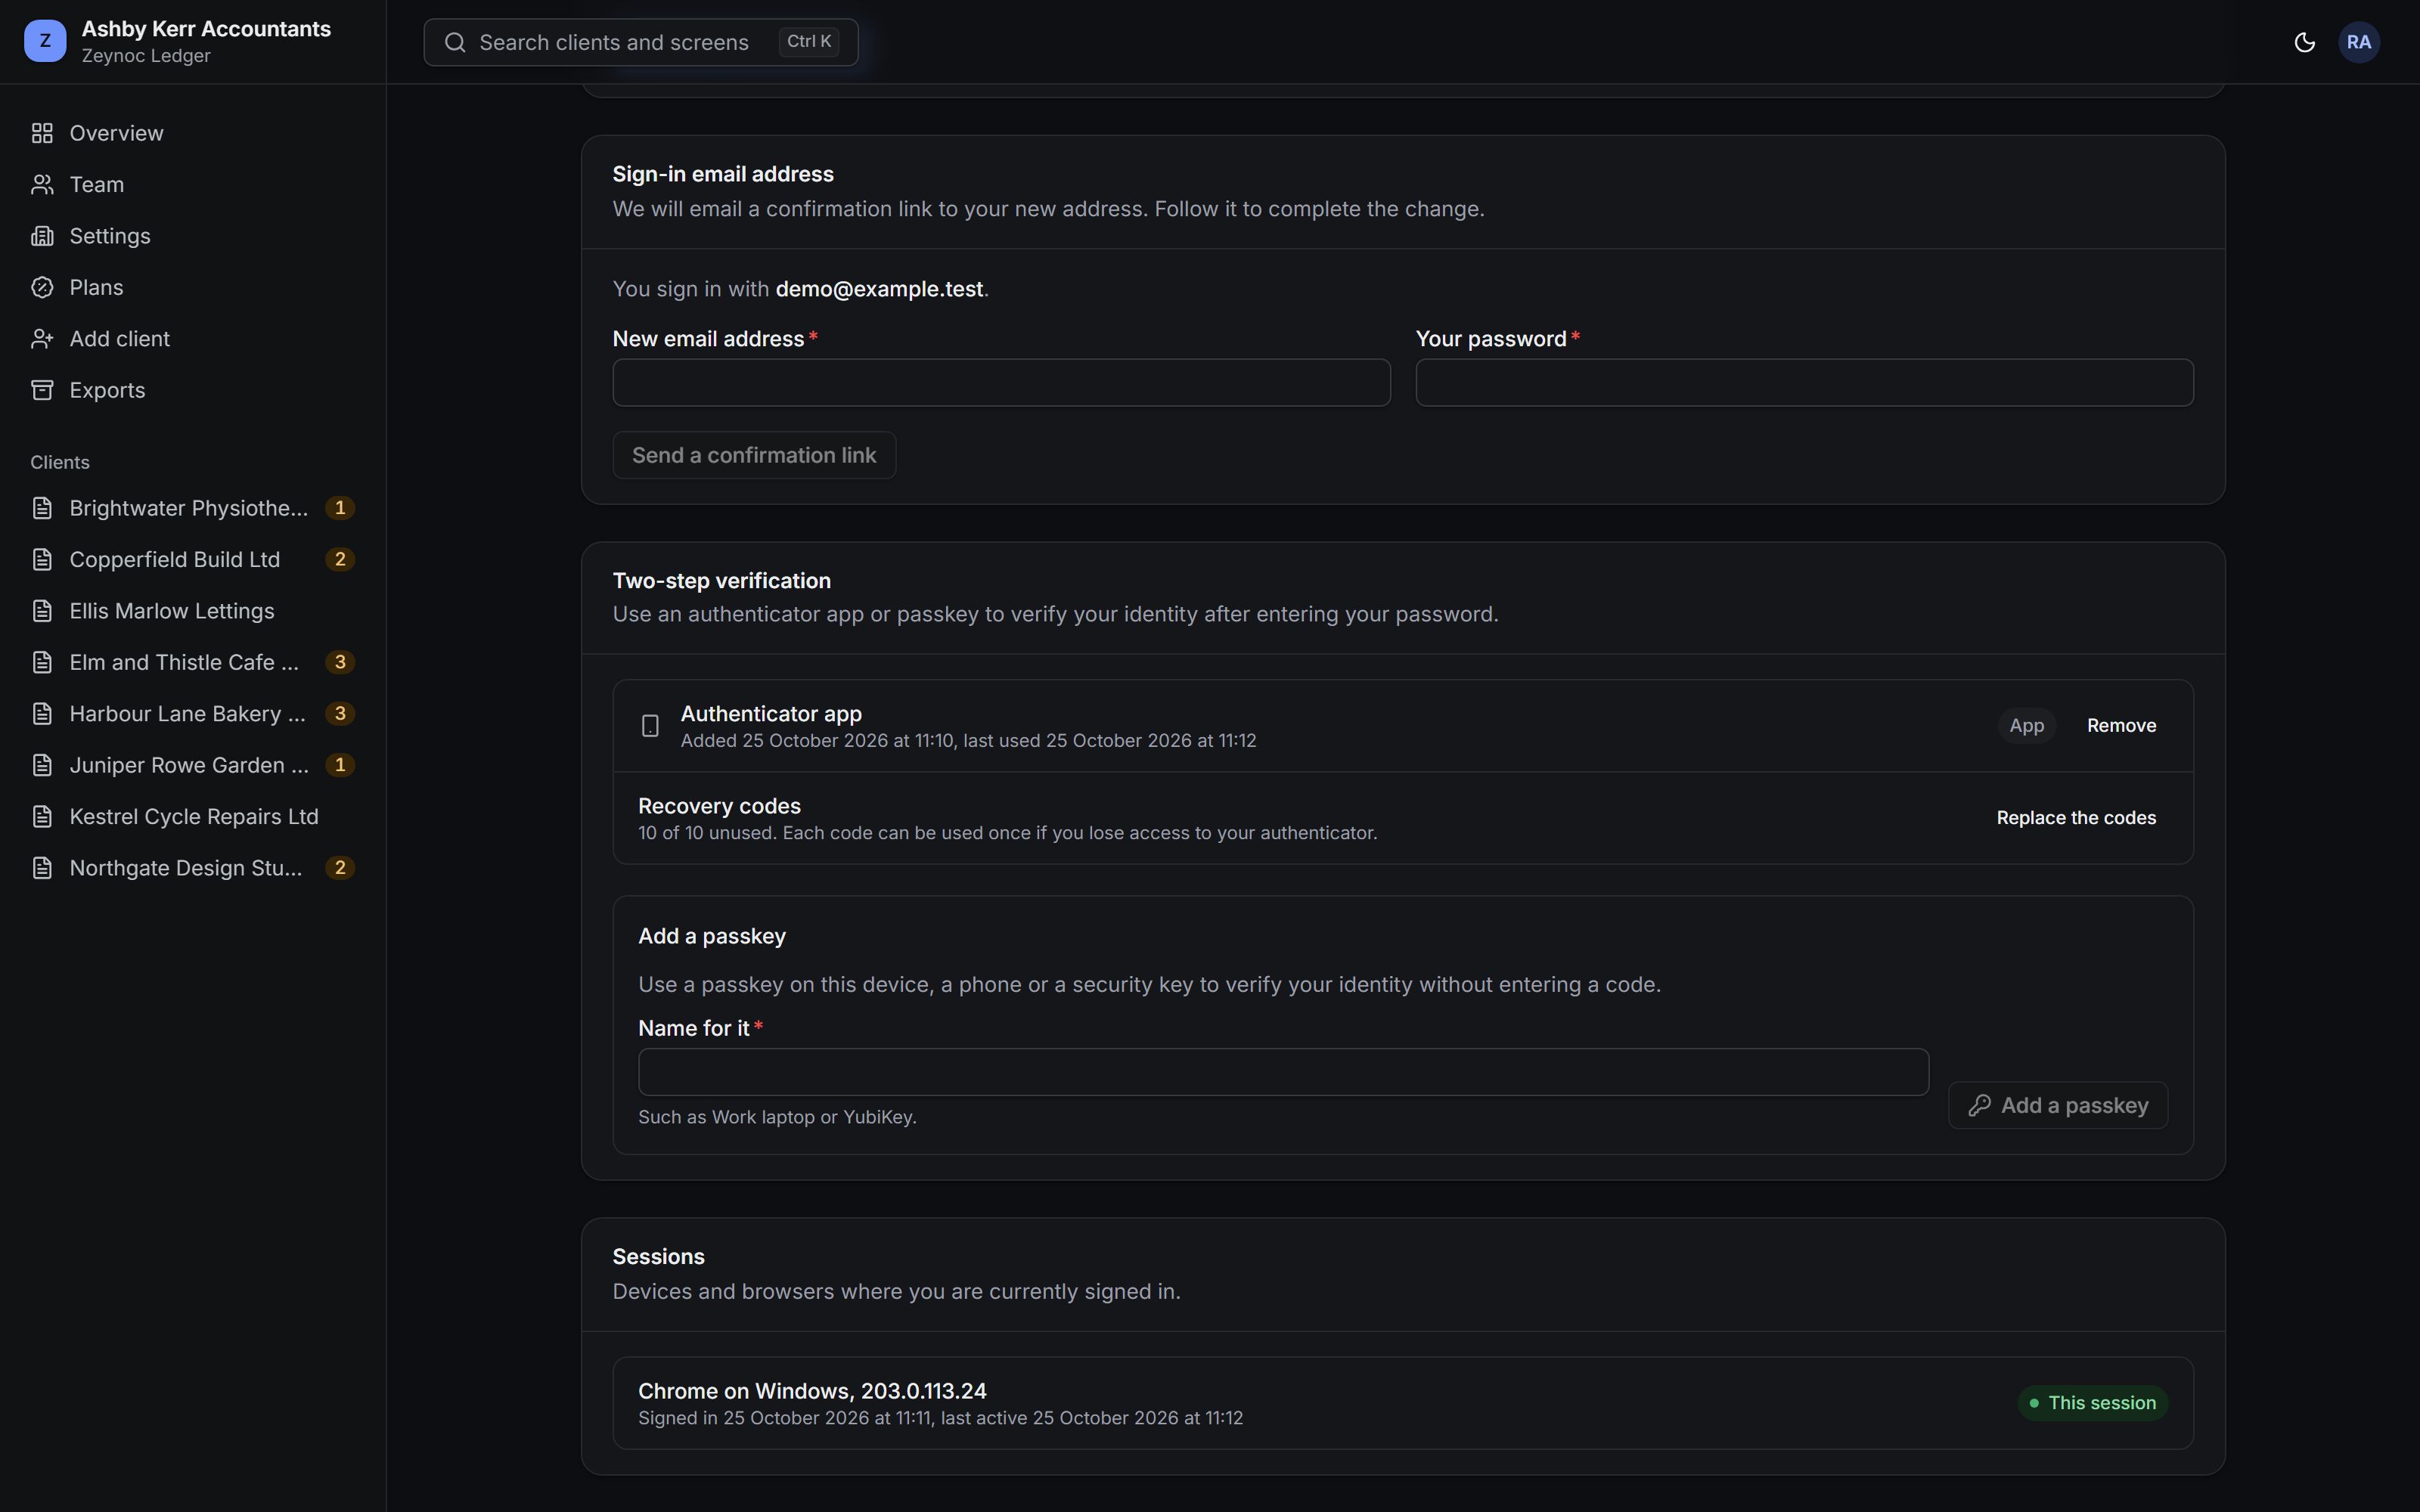
An authenticator app or a passkey is required before a person can do anything else. Text message codes are not offered.
Asked again before it matters
Submitting a VAT return, removing an HMRC connection and the other actions that cannot be undone need a fresh second factor from the last five minutes.
New devices announced
A sign in from a new device is announced by email, and repeated wrong passwords lock the account. Passwords are stored only as argon2id hashes.
03
Records you can rely on
What was posted, filed and changed stays as it was, with the name of the person who did it.
An audit trail that shows tampering
Every change is recorded with who made it and what it was before. Each practice's trail is hash chained, so a record altered afterwards fails the check that runs every night.
A ledger that only adds
Journals are never edited or deleted, only reversed. A filed VAT return and the period behind it are locked by the database.
Roles and grants
Staff roles decide what each person can do, clients can be granted to named staff, and client users see only their own books.
04
Banks, HMRC and payments
Connections to outside services hold the least access they need.
Read only bank feeds
Live feeds come through Plaid, a regulated Open Banking provider, and can read transactions only. Nothing in Zeynoc Ledger can move money from a bank account.
Payments through Stripe
Invoice payments go straight to your client's own Stripe account. Zeynoc never holds the money and takes no share of a payment.
Short lived document links
A document is downloaded through a link that works once and expires after five minutes, so a forwarded link opens nothing.
Responsible disclosure
Found a security issue in Zeynoc Ledger? Please tell us privately first, with enough detail to reproduce it, and give us a reasonable time to fix it before you share it.
Zeynoc Ledger does not hold security certifications today. If your practice needs details for its own review, write to us.